Share this post
The Ultimate AI Tax Compliance Checklist: Navigating SOC 2 & 7216
To use AI on client tax data compliantly, a firm needs two things. First, vendors whose security controls are independently audited under SOC 2. Second, a workflow that follows IRC Section 7216, which limits how preparers use and disclose tax return information and requires written client consent for most uses beyond preparing the return. The checklist below covers data mapping, access controls, consent, monitoring, and breach response.
AI now touches nearly every piece of client data, including Social Security numbers, income statements, and bank records. That means more efficiency, but it also means more exposure. Every new system in your workflow is another potential crack out of which sensitive data could leak.
Two rules matter most here:
- SOC 2: Keeps your systems honest and your controls tight.
- IRC Section 7216: Keeps you out of fines, lawsuits, and jail.
This isn’t theory. Breaches are rising. The IRS has no patience, and clients have even less. This checklist shows how to stay compliant while putting AI to work in your firm.
Why do SOC 2 and IRC 7216 matter in AI tax workflows?
Although SOC 2 and 7216 weren’t written for AI, they now define how AI fits into tax prep.
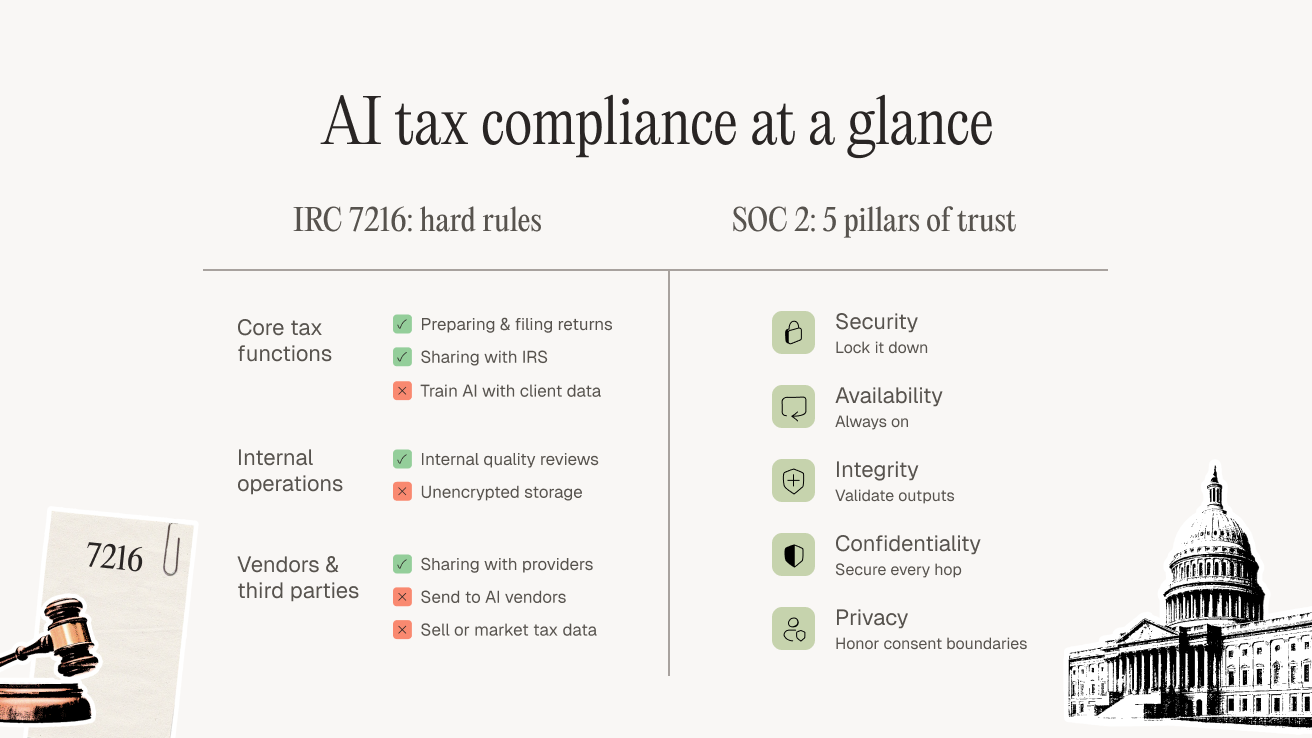
- SOC 2: The AICPA’s standard for system security, availability, processing integrity, confidentiality, and privacy.
- IRC 7216: Federal law that tells preparers exactly what they can and can’t do with client data.
Break either and you risk:
- Breaches when data jumps between platforms
- Centralized stores of client data becoming a single point of failure
- Penalties, lawsuits, and reputational damage you don’t bounce back from
AI doesn’t reduce these risks. If you’re sloppy, it multiplies them.
What does IRC section 7216 allow and prohibit?
7216 is simple. Client data is for preparing tax returns, period. Anything else requires explicit written consent (the IRS Section 7216 information center has the details).
Allowed under IRC section 7216:
- Preparing and filing tax returns
- Sharing with the IRS
- Internal quality reviews
- Sharing with software providers under proper agreements
Not allowed:
- Handing data to AI vendors without consent
- Using client data to train your model
- Selling or marketing based on tax data
- Storing unencrypted files in unauthorized systems
Penalties:
- Criminal fines up to $1,000 per offense and up to a year in jail
- Civil penalties of $250 per violation, up to $10,000 annually per preparer (26 U.S.C. § 6713)
Consent forms must spell out:
- What data is used
- Who touches it
- Why it’s used
- Expiration date
- That signing is voluntary
And yes, you must keep them for three years. No shortcuts.
What do the SOC 2 principles mean for tax firms using AI?
SOC 2 measures a system against five trust services criteria, and each one maps to a concrete control in an AI workflow.
SOC 2 runs on five pillars. Apply them ruthlessly:
- Security: Lock it down. MFA, encryption, access logs. No exceptions.
- Availability: AI won’t save you if systems go dark in March. Keep backups, practice redundancy, and use uptime monitoring. Test it.
- Processing Integrity: AI outputs need validation. Test them against real-world returns, not dummy data. And keep all audit trails.
- Confidentiality: Utilize role-based access and data segregation. Every system hop is a risk, so secure each one.
- Privacy: Collect only data that’s needed. Honor consent boundaries. Don’t hoard data just because AI makes it easy.
What should an AI tax compliance checklist include?
Five steps: map your data flow, lock down access, get explicit consent, monitor constantly, and drill breach response.
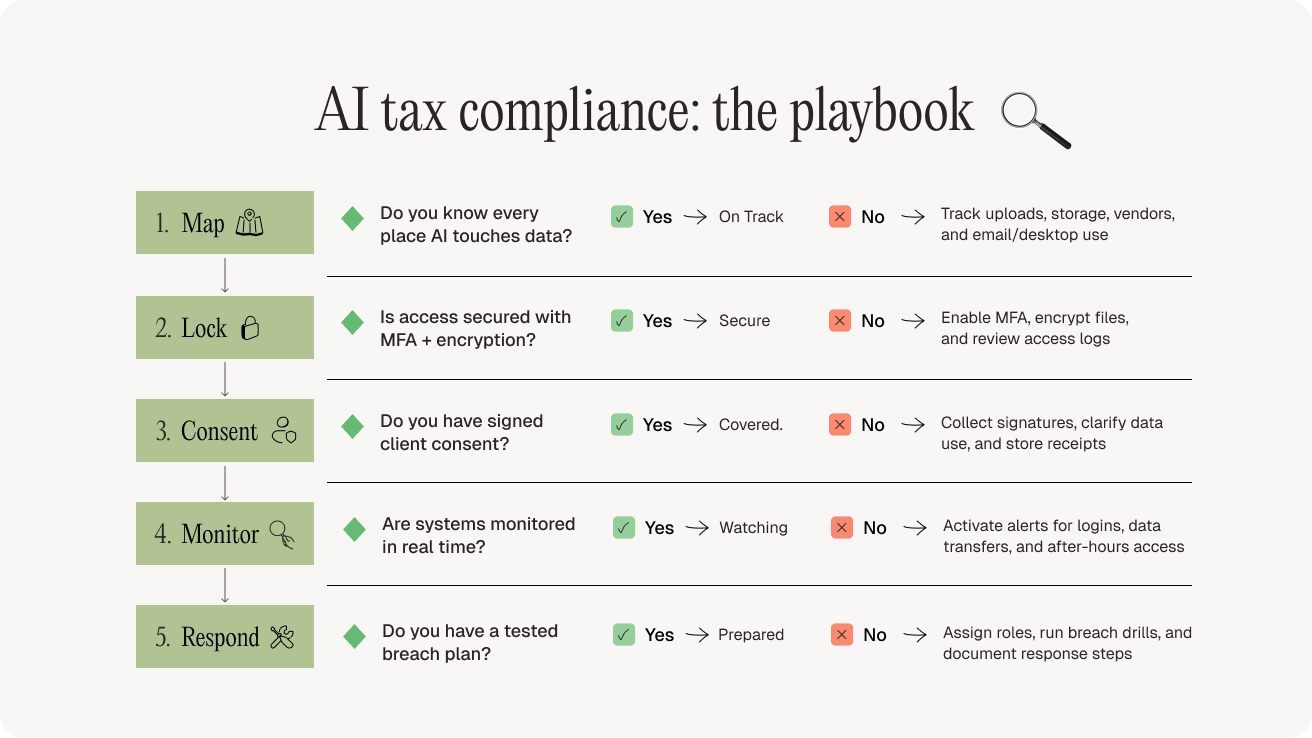
- Map your data flow. Document where AI touches tax data, like uploads, extraction, storage, and third-party vendors. Don’t forget “temporary” storage like email or desktop folders.
- Lock down access. Enforce MFA, encrypt everything, keep logs, and review them. If you can’t prove who accessed data and when, you’re exposed.
- Get explicit consent. If AI touches client data, get signatures up front. Spell out what the system does, who sees it, and why. Keep the receipts.
- Monitor constantly. Watch for alerts for failed logins, large transfers, and access after hours. If you’re not watching in real time, you’re already behind.
- Drill breach response. Have a plan. Know who locks down systems, who calls clients, and who files reports. Run practice drills. Chaos is not a strategy.
Does it matter where AI processes client data?
Where data is processed matters. Offshore use isn’t banned, but it’s a minefield.
- Consent: Offshore requires explicit disclosure
- Data transfer: More layers of security
- Jurisdiction: Good luck enforcing U.S. laws overseas
- Monitoring: Harder to audit
Even cloud servers outside the U.S. count as offshore. If your vendor won’t tell you where the data lives, assume the worst.
What should a firm do after a data breach?
Notify the right people fast, document everything, and close the gap.
Breaches happen in the cracks. When they do, responding with speed is everything. Take these steps:
- Notify fast. The IRS (through your local stakeholder liaison, per the IRS data theft guidance for tax professionals), state regulators. Some states demand notice within 15 days.
- Document everything. What happened, what data, what you did. Keep detailed records.
- Fix it. Update controls, close the gap, and renegotiate vendor agreements if necessary.
Delay, and you’re compounding the damage legally and reputationally.
How do you stay compliant while scaling?
Growth multiplies risk. More staff can mean more systems and more cracks. Stay ahead by:
- Automating monitoring
- Training staff regularly
- Keeping procedures documented and enforced
- Vetting every vendor (no black boxes allowed)
Filed was built with security in mind. It’s AI tax prep that moves returns faster while keeping SOC 2 and 7216 compliance baked in.
How do firms build trust with secure AI tax prep?
Compliance isn’t a box you check once. It’s ongoing. Technology shifts, laws update, and threats evolve. The firms that take this seriously will win client trust, and that’s the currency that actually matters.
At Filed, security is at the core of everything we do. We’re SOC 2 compliant and ISO 27001 certified, and all data is stored on servers in the United States, encrypted at rest and in transit. Our AI providers process client data under no-training and zero data retention terms, so they don’t train on it or keep it, and we never train models on your data.
Filed makes compliance practical. Filed Prep prepares returns and Filed Reviewer checks them against the source documents before sign-off. Fast returns, protected data, audit-ready trails. That’s how you scale without risking your license.
Frequently asked questions
What penalties come with 7216 violations?
Up to $1,000 and a year in jail per offense, plus $250 civil fines per violation (capped at $10,000 annually).
How often should firms review AI security measures?
At least annually, and every time you add or change an AI tool.
What consent language is required?
Be explicit: what data, how it’s used, who touches it, and how long it’s kept. Generic forms don’t cut it.
Do state laws add more rules?
Yes. Many states set stricter consent and breach timelines than the IRS. Know your jurisdiction.
What’s non-negotiable when sharing data with AI vendors?
Encryption, access controls, signed data use agreements, and verified security certifications.
Is Filed SOC 2 compliant?
Yes. Filed is SOC 2 compliant and ISO 27001 certified. SOC 2 and ISO reports are available under NDA.
That’s the compliance checklist firms actually need in 2025. SOC 2 keeps your systems tight. 7216 keeps you legal. Filed makes both non-negotiable while giving you speed at scale.
Subscribe to our newsletter
Explore our latest insights
Discover valuable articles to enhance your knowledge.